This report is based on an audit of an unknown smart contract. No source code was provided for analysis, therefore, a comprehensive security assessment of specific vulnerabilities, architecture, and economic models could not be performed. The findings below represent general security best practices applicable to any EVM smart contract.
Honeypot, rug-pull and ownership checks
Is Basecat a Scam?
Not verified
This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →This report is based on an audit of an unknown smart contract.
Read the full analysis- Ownership status UNKNOWN
- Mint capability UNKNOWN
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- Token age < 30 days
Exact factors
- Ownership status UNKNOWN (owner could not be resolved)
- Mint capability UNKNOWN (implementation ABI unreadable)
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- Token age < 30 days (still settling)
Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed
Security Checklist
as of audit · Sep 4Holders
as of audit · Sep 4, 2026- Contractstreasury, vesting, bridge, staking7.5%
- Walletsanonymous holders, free to sell7.6%
- Everyone elsethe rest of the supply84.8%
How holder types affect the score
Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.
Holder balances as recorded by the audit of Sep 4, 2026
Liquidity
as of audit · Sep 4- Uniswap v4ETHAnalysed$999.3K52.0%
- Uniswap v3WETH$342.7K17.8%
- Uniswap v4USDC$312.2K16.2%
- Uniswap v3USDC$92.5K4.8%
- Uniswap v4ETH$66.5K3.5%
- Uniswap v4ETH$47.9K2.5%
Show 4 more pairs
The 20 remaining pairs hold $13.7K between them and are not listed. The risk score reads depth across every pair.
The LP tokens of the analysed pool are not locked or burned, so whoever holds them can withdraw that liquidity.
0xe005…55630x82f6…c6740x5265…52f20x610e…1b650xd847…d6800xcca0…032c0x3739…e8420xee5d…85e40x1222…6d5f0x4108…972aNo privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.
Security Findings
InfoComprehensive Testing is Essential
Without source code, the extent of testing (unit, integration, fuzzing, formal verification) cannot be verified. Inadequate testing is a common source of vulnerabilities, leading to unexpected behavior or exploits.I-01
Issue
Without source code, the extent of testing (unit, integration, fuzzing, formal verification) cannot be verified. Inadequate testing is a common source of vulnerabilities, leading to unexpected behavior or exploits.
Fix
Ensure a comprehensive testing suite covers all critical functionalities and edge cases. Implement continuous integration/continuous deployment (CI/CD) pipelines with automated security checks. Consider formal verification for critical components.
Status
Unresolved
InfoAdherence to Secure Coding Standards
The absence of source code prevents assessment of adherence to secure coding best practices, such as reentrancy guards, integer overflow/underflow checks, and proper error handling. Violations can lead to severe vulnerabilities.I-02
Issue
The absence of source code prevents assessment of adherence to secure coding best practices, such as reentrancy guards, integer overflow/underflow checks, and proper error handling. Violations can lead to severe vulnerabilities.
Fix
All smart contract code should strictly follow established secure coding guidelines. Utilize battle-tested libraries (e.g., OpenZeppelin Contracts) and ensure all external calls are handled securely, especially regarding reentrancy and gas limits.
Status
Unresolved
InfoRobust Access Control Mechanisms
Without code, the implementation of access control for sensitive functions cannot be evaluated. Weak or improperly configured access control can allow unauthorized users to perform critical operations, leading to asset loss or system manipulation.I-03
Issue
Without code, the implementation of access control for sensitive functions cannot be evaluated. Weak or improperly configured access control can allow unauthorized users to perform critical operations, leading to asset loss or system manipulation.
Fix
Implement strict role-based access control (RBAC) for all privileged functions. Utilize Ownable or AccessControl patterns, and consider multi-signature wallets for critical administrative actions to prevent single points of failure.
Status
Unresolved
InfoConsideration of Upgradeability Patterns
The contract's upgradeability status and pattern (e.g., UUPS, Transparent) are unknown. Improperly implemented upgrade mechanisms can introduce significant risks, including storage collisions, logic errors, or even bricking the contract.I-04
Issue
The contract's upgradeability status and pattern (e.g., UUPS, Transparent) are unknown. Improperly implemented upgrade mechanisms can introduce significant risks, including storage collisions, logic errors, or even bricking the contract.
Fix
If the contract is intended to be upgradeable, ensure a well-understood and securely implemented proxy pattern is used. Thoroughly test upgrade paths, including storage layout compatibility, and ensure upgrade permissions are secured, ideally via a multi-signature wallet or governance.
Status
Unresolved
Analysis
AI Copilotas of audit · Sep 4Due to the absence of smart contract source code, a detailed technical analysis covering architecture (7.1), code security (7.2), and access control (7.3) could not be conducted. Therefore, no specific strengths or weaknesses related to implementation details can be reported. General best practices for secure coding and robust access control are assumed to be critical for any deployed contract.
Without access to the contract's source code, an evaluation of its economic model (7.4) and governance mechanisms (7.5) is not possible. Key considerations such as tokenomics, fee structures, and decision-making processes remain unknown. External dependencies (7.6) and their potential impact on the protocol's stability also cannot be assessed.
The upgradeability strategy (7.7) and operational procedures (7.8) for the contract could not be determined without source code. It is crucial for any production system to have a well-defined and secure upgrade path, if applicable, and clear operational guidelines for administrators, including multi-signature requirements for critical actions.
For any smart contract deployment, it is paramount to conduct thorough security audits on the complete and final source code.
Implement robust testing frameworks, including unit, integration, and fuzz testing. Ensure all critical functions are protected by multi-signature wallets and that emergency pause mechanisms are in place. Regularly review and update dependencies to mitigate known vulnerabilities.
Contract & Record
Free for any token on the record. It links to this page and always shows the current score and the date it was checked.
- Aug 30, 202613Low
Score changes are recorded as dated snapshots — history is append-only and cannot be edited.
Frequently Asked Questions
What is the BASECAT contract address?
The Basecat contract on Base is 0xb2000000000000000000004c27f6523082f41d01. Compare it with the address the project itself publishes before trading: other contracts can carry the same name and ticker.
Is Basecat a scam?
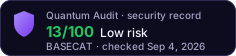
Quantum Audit's risk score for Basecat is 13/100 (Low risk) as of Sep 4, 2026, computed by a deterministic function from on-chain facts — Contract verified: Verified; Liquidity lock: Not locked; Upgradeability: Fixed code; Honeypot: None found; Buy / sell tax: 0% / 0%. A score is a dated snapshot of those facts, not a guarantee; each one is listed on this page.
Is BASECAT liquidity locked?
Liquidity lock: Not locked (as of Sep 4, 2026). Total DEX liquidity: $1.92M.
Who holds BASECAT?
As of Sep 4, 2026, the 10 largest holders own 15.2% of the supply. The Holders section on this page shows who they are by holder type.
Would You Like a More Detailed Audit of Basecat?
Paste the contract address into our AI-powered scanner for a deeper real-time report — free, with every scoring factor shown.
Get Detailed Audit Is this your token? Publish your own audit on this page