Quantum Audit Logo
Launch App

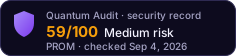
On-chain security analysis — is it a scam or legit?

Is Prometeus Safe?

PROMBNB Chain
Not verified This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →
Last checked Sep 4, 2026 · 1 audit on record
SummaryAI Copilot

The Prometeus (PROM) Token contract is a standard BEP20 implementation with Ownable access control and SafeMath for arithmetic operations.

Read the full analysis
What raised the score
  • Ownership not renounced — owner is an EOA
  • Top-10 concentration > 70%
  • Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
  • LP top1 unlocked holder = 99.7%
  • LP top3 unlocked holders = 100.0%
  • 1 Low finding(s) from audit
Exact factors
  • Ownership NOT renounced — owner is an EOA (single private key)
  • Top-10 concentration > 70% (98.1% total → 98.0% effective; 97.9% in EOAs, 0.2% in contracts — extreme)
  • Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
  • LP top1 unlocked holder = 99.7% (independent LP — depth risk, pool = 99% of DEX liquidity)
  • LP top3 unlocked holders = 100.0% (independent LP — depth risk, pool = 99% of DEX liquidity)
  • 1 Low finding(s) from audit

Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed

Security Checklist

as of audit · Sep 45 of 7 checks passed
Contract verifiedVerified
OwnershipRetained
MintNo mint
Liquidity lockNot locked
UpgradeabilityFixed code
HoneypotNone found
Buy / sell tax0% / 0%

Holders

as of audit · Sep 4, 2026
97.9%Wallets1.9%
97.9%Wallets
ContractsWalletsEveryone elseBubble area = share of supply
98.1%of supply sits with the top 10 holders
  • Contractstreasury, vesting, bridge, staking0.2%
  • Walletsanonymous holders, free to sell97.9%
  • Everyone elsethe rest of the supply1.9%
Effective concentrationwhat the score reads98.0%
How holder types affect the score

Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.

Holder balances as recorded by the audit of Sep 4, 2026

Liquidity

as of audit · Sep 4$133.6K across 9 pairs
LP tokensNot locked

The LP tokens of the analysed pool are not locked or burned, so whoever holds them can withdraw that liquidity.

Analysed pool$132.9KShare of depth99.4%
Top-1 Unlocked Holder99.7%
Top-3 Unlocked100.0%
Unlocked LP held by
0x2ba8…a01e0xa80e…61f00xf587…3d290x5e91…fac10x4125…df6c0xa873…45880xba64…7242

No privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.

Security Findings

1 Low1 Info
Low

Potential approve Race Condition (Mitigated)

The standard ERC-20 approve function is susceptible to a front-running attack where a malicious actor can observe a transaction to decrease an allowance and front-run it, transferring the original approved amount before the allowance is reduced. This could lead to a user approving a larger amount than intended. While the contract provides increaseAllowance and decreaseAllowance functions to mitigate this by allowing atomic adjustments, the base approve function still exists and can be used directly.L-01

Issue

The standard ERC-20 approve function is susceptible to a front-running attack where a malicious actor can observe a transaction to decrease an allowance and front-run it, transferring the original approved amount before the allowance is reduced. This could lead to a user approving a larger amount than intended. While the contract provides increaseAllowance and decreaseAllowance functions to mitigate this by allowing atomic adjustments, the base approve function still exists and can be used directly.

Fix

Educate users to primarily use increaseAllowance and decreaseAllowance instead of directly calling approve when modifying an existing allowance. For new approvals, approve is safe. Ensure any external integrations or dApps interacting with this token prioritize the use of the safer allowance adjustment functions.

Status

Unresolved

Info

Use of Older Solidity Compiler Version

The contract is compiled with Solidity version 0.5.16. While functional, this version is older. Newer Solidity versions (e.g., 0.8.x) offer significant improvements, including built-in overflow/underflow checks (making SafeMath redundant and potentially saving gas), better optimizer performance, and enhanced security features.I-01

Issue

The contract is compiled with Solidity version 0.5.16. While functional, this version is older. Newer Solidity versions (e.g., 0.8.x) offer significant improvements, including built-in overflow/underflow checks (making SafeMath redundant and potentially saving gas), better optimizer performance, and enhanced security features.

Fix

Consider upgrading the Solidity compiler version to a more recent stable release (e.g., 0.8.x) for future deployments or contract updates. This would allow for removal of the SafeMath library, reducing bytecode size and gas costs, and leveraging modern compiler optimizations.

Status

Unresolved

Analysis

AI Copilotas of audit · Sep 4
Executive SummaryWhat the contract is and what the review found

The Prometeus (PROM) Token contract is a standard BEP20 implementation with Ownable access control and SafeMath for arithmetic operations. The contract exhibits good adherence to BEP20 standards and includes common security practices such as zero-address checks and event emissions. Identified risks are minor, primarily related to the use of an older Solidity compiler version and a low-severity approve race condition, which is partially mitigated by helper functions.
Technical8/10Low risk

The technical architecture (7.1 Architecture) is a straightforward BEP20 token with Ownable pattern. Code security (7.2 Code Security) is strong, utilizing SafeMath to prevent integer overflows/underflows and including necessary zero-address checks in critical transfer and approval functions. Access control (7.3 Access Control) is standard for an Ownable token, restricting only ownership transfers and renunciations. A minor issue is the use of an older Solidity compiler (0.5.16), which could be updated for better optimizations and built-in safety features. The contract also includes increaseAllowance and decreaseAllowance functions, which help mitigate the classic ERC-20 approve race condition.

Governance1/10High risk

The economic model (7.4 Economic) is a fixed-supply token with all tokens minted to the deployer at creation, which is a standard distribution model. There are no complex economic mechanisms, staking, or lending pools within this contract. Governance (7.5 Governance) is limited to the Ownable pattern, allowing the owner to transfer or renounce ownership. There are no external dependencies (7.6 External) that could introduce economic or governance risks, as the contract only interacts with the IBEP20 interface for standard token operations.

Upgrades6/10Medium risk

The contract is not designed to be upgradeable (7.7 Upgrades), meaning there are no proxy patterns (e.g., UUPS, Transparent, Beacon) implemented. This eliminates upgrade-related risks such as proxy misconfigurations or logic contract vulnerabilities introduced during upgrades. The contract is immutable once deployed, providing a stable and predictable operational environment (7.8 Operations).

Final RecommendationWhat to do about this score

It is recommended to consider migrating to a newer Solidity compiler version (e.g., 0.8.x) to leverage built-in overflow/underflow checks and gas optimizations, making SafeMath redundant.

While the contract includes mitigation for the approve race condition, users should still be educated on the best practices of using increaseAllowance and decreaseAllowance instead of directly calling approve when adjusting existing allowances. Regular security reviews of any interacting contracts are also advised.

Contract & Record

1 audit on record
TypePROMToken
NetworkBNB Chain
Token age1y
Contract0xaf53…afd5
Deployer0xe082…18de
Badge for your website
Prometeus security record badge

Free for any token on the record. It links to this page and always shows the current score and the date it was checked.

Audit History
  1. Sep 1, 202659Medium

Score changes are recorded as dated snapshots — history is append-only and cannot be edited.

Frequently Asked Questions

What is the PROM contract address?

The Prometeus (PROM) contract on BNB Chain is 0xaf53d56ff99f1322515e54fdde93ff8b3b7dafd5. Compare it with the address the project itself publishes before trading: other contracts can carry the same name and ticker.

Is Prometeus a scam?

Quantum Audit's risk score for Prometeus is 59/100 (Medium risk) as of Sep 4, 2026, computed by a deterministic function from on-chain facts — Contract verified: Verified; Ownership: Retained; Mint: No mint; Liquidity lock: Not locked; Upgradeability: Fixed code; Honeypot: None found; Buy / sell tax: 0% / 0%. A score is a dated snapshot of those facts, not a guarantee; each one is listed on this page.

Is PROM liquidity locked?

Liquidity lock: Not locked (as of Sep 4, 2026). Total DEX liquidity: $133.6K.

Who holds PROM?

As of Sep 4, 2026, the 10 largest holders own 98.1% of the supply. The Holders section on this page shows who they are by holder type.

Would You Like a More Detailed Audit of Prometeus?

Our AI-powered scanner gives you a deeper, real-time smart contract analysis — free, with every scoring factor shown.

Get Detailed Audit Is this your token? Publish your own audit on this page