The MeyNetwork token contract is implemented using standard, battle-tested OpenZeppelin ERC20, ERC20Burnable, and ERC20Permit components. No custom logic was provided for analysis, so the assessment focuses on the inherent security of these foundational libraries. The contract benefits from robust security practices embedded in OpenZeppelin, including safe arithmetic and a secure permit mechanism. Potential risks primarily stem from design choices such as centralization of token supply control if minting is owner-controlled, and the immutability of the contract logic.
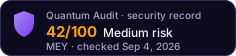
On-chain security analysis — is it a scam or legit?
Is Mey Network Safe?
Not verified
This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →The MeyNetwork token contract is implemented using standard, battle-tested OpenZeppelin ERC20, ERC20Burnable, and ERC20Permit components.
Read the full analysis- Ownership not renounced — owner is an EOA
- Top-10 concentration > 50%
- 2 Low finding(s) from audit
Exact factors
- Ownership NOT renounced — owner is an EOA (single private key)
- Top-10 concentration > 50% (86.3% total → 69.9% effective; 58.9% in EOAs, 27.3% in contracts — heavy)
- 2 Low finding(s) from audit
Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed
Security Checklist
as of audit · Sep 4Holders
as of audit · Sep 4, 2026- Contractstreasury, vesting, bridge, staking27.3%
- Walletsanonymous holders, free to sell58.9%
- Everyone elsethe rest of the supply13.7%
How holder types affect the score
Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.
Holder balances as recorded by the audit of Sep 4, 2026
Liquidity
as of audit · Sep 4- Uniswap v3WETHAnalysed$133.8K50.5%
- AerodromeWETH$126.6K47.8%
- AerodromeWETH$3.8K1.4%
- Uniswap v2WETH$3950.1%
- Uniswap v3USDT$1330.1%
The risk score reads depth across every pair.
The LP tokens of the analysed pool are locked or burned.
0x1cbb…b1a40x7f42…98d80x8cf6…9cdf0x6313…1a600x774c…1a79No privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.
Security Findings
LowCentralized Control over Token Supply (Potential)
The underlying ERC20 contract includes internal _mint and _burn functions. If the MeyNetwork contract exposes the _mint function to an owner or a privileged role, this introduces a centralized point of control over the token's total supply. An attacker gaining control of this owner key could arbitrarily inflate the supply, devaluing existing tokens. While common for many tokens, this represents a centralization risk (7.3 Access Control, 7.5 Governance).L-01
Issue
The underlying ERC20 contract includes internal _mint and _burn functions. If the MeyNetwork contract exposes the _mint function to an owner or a privileged role, this introduces a centralized point of control over the token's total supply. An attacker gaining control of this owner key could arbitrarily inflate the supply, devaluing existing tokens. While common for many tokens, this represents a centralization risk (7.3 Access Control, 7.5 Governance).
Fix
Clearly document the role and responsibilities of any address capable of minting or burning tokens. If possible, consider implementing a timelock for minting operations or a multi-signature wallet for the controlling address to reduce single points of failure. If decentralization is a goal, consider removing or restricting minting capabilities after initial supply distribution.
Status
Unresolved
LowImmutability of Contract Logic
The contract is not implemented using an upgradeable proxy pattern (7.7 Upgrades). This means that once deployed, the contract's logic cannot be modified. While this provides certainty and removes upgrade-related risks, it also implies that any discovered bugs, vulnerabilities, or desired feature enhancements would necessitate a new contract deployment and a potentially complex token migration process for users (7.7 Upgrades).L-02
Issue
The contract is not implemented using an upgradeable proxy pattern (7.7 Upgrades). This means that once deployed, the contract's logic cannot be modified. While this provides certainty and removes upgrade-related risks, it also implies that any discovered bugs, vulnerabilities, or desired feature enhancements would necessitate a new contract deployment and a potentially complex token migration process for users (7.7 Upgrades).
Fix
Ensure comprehensive testing, including unit, integration, and fuzz testing, is performed prior to deployment. Consider engaging in formal verification for critical components. Clearly communicate the immutable nature of the contract to users and stakeholders, emphasizing the importance of initial security audits.
Status
Unresolved
InfoAdherence to OpenZeppelin Standards
The contract is built upon well-audited and widely adopted OpenZeppelin ERC20, ERC20Burnable, and ERC20Permit libraries. This significantly reduces the likelihood of common vulnerabilities such as reentrancy, integer overflows/underflows, and standard ERC20 compliance issues (7.2 Code Security). The use of these battle-tested components contributes to a strong security foundation.I-01
Issue
The contract is built upon well-audited and widely adopted OpenZeppelin ERC20, ERC20Burnable, and ERC20Permit libraries. This significantly reduces the likelihood of common vulnerabilities such as reentrancy, integer overflows/underflows, and standard ERC20 compliance issues (7.2 Code Security). The use of these battle-tested components contributes to a strong security foundation.
Fix
Continue to monitor OpenZeppelin security advisories and updates. Ensure that any custom logic added to the MeyNetwork contract maintains the high security standards set by the inherited OpenZeppelin components.
Status
Unresolved
InfoRobust Permit Mechanism
The ERC20Permit implementation correctly utilizes EIP-712 for structured data signing and incorporates nonces (_useNonce) to prevent signature replay attacks. This design ensures that each permit signature can only be used once, enhancing the security and usability of gasless approvals (7.2 Code Security).I-02
Issue
The ERC20Permit implementation correctly utilizes EIP-712 for structured data signing and incorporates nonces (_useNonce) to prevent signature replay attacks. This design ensures that each permit signature can only be used once, enhancing the security and usability of gasless approvals (7.2 Code Security).
Fix
No specific recommendation is needed for the ERC20Permit implementation itself, as it follows best practices. Users should be educated on how to safely interact with permit signatures and verify the details before signing.
Status
Unresolved
Analysis
AI Copilotas of audit · Sep 4The contract leverages battle-tested OpenZeppelin libraries for its ERC20, Burnable, and Permit functionalities, ensuring a high degree of code security and adherence to standards (7.2 Code Security). The implementation correctly uses unchecked blocks where arithmetic safety is guaranteed by prior checks, preventing integer overflow/underflow vulnerabilities. The ERC20Permit mechanism is robust, utilizing EIP-712 and nonces to prevent signature replay attacks (7.2 Code Security). No significant technical vulnerabilities were identified within the provided OpenZeppelin components.
The token's economic model, based on the ERC20 standard, is straightforward and widely understood (7.4 Economic). The ERC20Permit functionality enhances user experience by allowing gasless approvals (7.4 Economic). If the MeyNetwork contract exposes the internal _mint function to an owner, it introduces a centralized point of control over the token supply, which could impact trust and economic stability (7.3 Access Control, 7.5 Governance). The absence of a pausable mechanism means that in case of an emergency, the contract cannot be halted (7.8 Operations).
The contract is not designed to be upgradeable, which eliminates the complexities and potential risks associated with proxy patterns and upgrade mechanisms (7.7 Upgrades). This provides certainty regarding the immutability of the contract's logic. The non-upgradeable nature means that any future bug fixes, feature enhancements, or protocol changes would necessitate a new contract deployment and a token migration process, which can be costly and disruptive for users (7.7 Upgrades).
It is recommended to carefully review the specific implementation of the MeyNetwork contract, particularly how _mint and _burn functions are exposed and controlled, to ensure appropriate access control and decentralization if desired.
Consider implementing a pausable mechanism for emergency situations if the project's risk model allows for such centralized control. For non-upgradeable contracts, thorough testing and formal verification are paramount before deployment, as logic cannot be altered post-launch.
Contract & Record
Free for any token on the record. It links to this page and always shows the current score and the date it was checked.
- Aug 30, 202642Medium
Score changes are recorded as dated snapshots — history is append-only and cannot be edited.
Would You Like a More Detailed Audit of Mey Network?
Our AI-powered scanner gives you a deeper, real-time smart contract analysis — free, with every scoring factor shown.
Get Detailed Audit Is this your token? Publish your own audit on this page