The AIW3Token contract is a standard ERC-20 implementation, inheriting from battle-tested OpenZeppelin libraries. The technical security of the code is high, with no critical vulnerabilities found. However, the initial token distribution model presents a significant economic centralization risk, as the entire supply is minted to a single address.
On-chain security analysis — is it a scam or legit?
Is AIW3 Safe?
Not verified
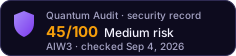
This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →The AIW3Token contract is a standard ERC-20 implementation, inheriting from battle-tested OpenZeppelin libraries.
Read the full analysis- Ownership status UNKNOWN
- Top-10 concentration > 30%
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top1 unlocked holder = 100.0%
- LP top3 unlocked holders = 100.0%
- Token age < 30 days
- 1 High finding(s) from audit
- 1 Low finding(s) from audit
Exact factors
- Ownership status UNKNOWN (owner could not be resolved)
- Top-10 concentration > 30% (87.6% total → 35.6% effective; 1.0% in EOAs, 86.6% in contracts — moderate)
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top1 unlocked holder = 100.0% (independent LP — depth risk)
- LP top3 unlocked holders = 100.0% (independent LP — depth risk)
- Token age < 30 days (still settling)
- 1 High finding(s) from audit
- 1 Low finding(s) from audit
Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed
Security Checklist
as of audit · Sep 4Holders
as of audit · Sep 4, 2026- Contractstreasury, vesting, bridge, staking86.6%
- Walletsanonymous holders, free to sell1.0%
- Everyone elsethe rest of the supply12.4%
How holder types affect the score
Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.
Holder balances as recorded by the audit of Sep 4, 2026
Liquidity
as of audit · Sep 4The risk score reads depth across every pair.
The LP tokens of the analysed pool are not locked or burned, so whoever holds them can withdraw that liquidity.
0xc517…7bb2No privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.
Security Findings
HighCentralized Initial Token Distribution
The entire TOTAL_SUPPLY of 1,000,000,000 AIW3 tokens (10^9 * 10^18 wei) is minted to a single initialHolder address during contract deployment. This creates a single point of control for the entire token supply at launch, posing a significant economic risk (7.4 Economic). A large portion of the supply held by one entity can lead to market manipulation, concentrated selling pressure, or disproportionate influence in any future governance mechanisms (7.5 Governance).H-01
Issue
The entire TOTAL_SUPPLY of 1,000,000,000 AIW3 tokens (10^9 * 10^18 wei) is minted to a single initialHolder address during contract deployment. This creates a single point of control for the entire token supply at launch, posing a significant economic risk (7.4 Economic). A large portion of the supply held by one entity can lead to market manipulation, concentrated selling pressure, or disproportionate influence in any future governance mechanisms (7.5 Governance).
Fix
Implement a diversified token distribution strategy. This could involve vesting schedules, multiple initial distribution addresses, or a community-driven launch mechanism. If a single initialHolder is necessary, consider using a multi-signature wallet for this address to enhance security and decentralization of control. Clearly communicate the distribution plan to the community.
Status
Unresolved
LowRedundant Constant TOTAL_SUPPLY_WHOLE
The constant TOTAL_SUPPLY_WHOLE is declared with a value of 1_000_000_000 but is not utilized anywhere within the contract's logic. While harmless, it adds unnecessary code and could potentially lead to confusion if not clearly distinguished from TOTAL_SUPPLY (which includes decimals) by future developers or auditors (7.2 Code Security).L-01
TOTAL_SUPPLY_WHOLEIssue
The constant TOTAL_SUPPLY_WHOLE is declared with a value of 1_000_000_000 but is not utilized anywhere within the contract's logic. While harmless, it adds unnecessary code and could potentially lead to confusion if not clearly distinguished from TOTAL_SUPPLY (which includes decimals) by future developers or auditors (7.2 Code Security).
Fix
Remove the TOTAL_SUPPLY_WHOLE constant if it serves no functional purpose within the contract. If it is intended for off-chain informational use, consider adding a comment to clarify its role and prevent misinterpretation.
Status
Unresolved
InfoImmutability and Lack of Administrative Control
The AIW3Token contract is designed to be immutable, meaning it has no administrative functions such as pausing transfers, blacklisting addresses, or upgradeability (7.3 Access Control, 7.7 Upgrades). This design choice enhances decentralization and predictability, as the contract's behavior cannot be altered post-deployment. However, it also means that no emergency measures can be taken in the event of unforeseen circumstances, such as a major exploit in a DeFi protocol interacting with the token, or a critical bug discovered in the token's logic (though unlikely given OpenZeppelin's foundation).I-01
Issue
The AIW3Token contract is designed to be immutable, meaning it has no administrative functions such as pausing transfers, blacklisting addresses, or upgradeability (7.3 Access Control, 7.7 Upgrades). This design choice enhances decentralization and predictability, as the contract's behavior cannot be altered post-deployment. However, it also means that no emergency measures can be taken in the event of unforeseen circumstances, such as a major exploit in a DeFi protocol interacting with the token, or a critical bug discovered in the token's logic (though unlikely given OpenZeppelin's foundation).
Fix
Acknowledge this design choice and its implications. For a simple, non-governance token, immutability is often preferred for its security benefits. Ensure that all integrations and ecosystem partners are aware of the token's immutable nature and the absence of emergency controls.
Status
Unresolved
Analysis
AI Copilotas of audit · Sep 4The AIW3Token contract is built upon the latest OpenZeppelin ERC-20 standard (v0.8.20+), ensuring a robust and well-audited foundation (7.2 Code Security). The contract's logic is minimal, primarily extending the ERC-20 functionality with fixed constants and a single initial minting event in the constructor (7.1 Architecture). All arithmetic operations are handled safely, leveraging OpenZeppelin's unchecked blocks where appropriate after bounds checks, mitigating integer overflow/underflow risks. No complex external interactions or reentrancy vectors were identified.
The primary economic risk (7.4 Economic) stems from the initial token distribution, where the entire TOTAL_SUPPLY is minted to a single initialHolder address. This creates a highly centralized supply at launch, which could lead to significant market volatility or concentrated influence if the token were to be used in a governance model (7.5 Governance). The contract is not mintable after deployment, which is a positive for supply predictability. There are no administrative roles like pausers or blacklisters, which enhances decentralization but removes emergency control (7.3 Access Control).
The AIW3Token contract is not designed with upgradeability features (7.7 Upgrades). It is a simple, immutable ERC-20 token. This design choice eliminates all risks associated with upgrade mechanisms, such as proxy implementation bugs or administrative key compromise for upgrades. The contract's behavior is fixed upon deployment.
It is strongly recommended to implement a well-planned and transparent token distribution strategy to mitigate the high centralization risk associated with the initialHolder controlling the entire supply.
Consider a phased release or a multi-signature wallet for the initialHolder address to reduce single points of failure and build community trust. Additionally, ensure robust operational security for the initialHolder's private keys.
Contract & Record
Free for any token on the record. It links to this page and always shows the current score and the date it was checked.
- Sep 2, 202645Medium
Score changes are recorded as dated snapshots — history is append-only and cannot be edited.
Would You Like a More Detailed Audit of AIW3?
Our AI-powered scanner gives you a deeper, real-time smart contract analysis — free, with every scoring factor shown.
Get Detailed Audit Is this your token? Publish your own audit on this page