The USDe contract implements an ERC20 token with burnable and permit functionalities, utilizing OpenZeppelin's Ownable2Step for ownership management. A key feature is the minter role, which is exclusively authorized to mint new tokens. The contract's security is enhanced by using battle-tested OpenZeppelin libraries and a Timelock for the owner address. However, the centralized control over token supply via the minter and owner roles introduces significant economic and governance risks, as the token's stability relies heavily on the integrity of these privileged accounts and associated off-chain processes.
On-chain security analysis — is it a scam or legit?
Is USDe Safe?
Not verified
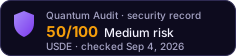
This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →The USDe contract implements an ERC20 token with burnable and permit functionalities, utilizing OpenZeppelin's Ownable2Step for ownership management.
Read the full analysis- Ownership not renounced — Timelock 24h delay
- Mintable supply — no cap found, dilution unbounded
- Top-10 concentration > 30%
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top1 unlocked holder = 59.1%
- LP top3 unlocked holders = 88.0%
- 1 High finding(s) from audit
- 1 Medium finding(s) from audit
- 1 Low finding(s) from audit
Exact factors
- Ownership NOT renounced — Timelock 24h delay
- Mintable supply — no cap found, dilution unbounded
- Top-10 concentration > 30% (95.0% total → 43.8% effective; 9.7% in EOAs, 85.3% in contracts — moderate)
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top1 unlocked holder = 59.1% (independent LP — depth risk, pool = 52% of DEX liquidity)
- LP top3 unlocked holders = 88.0% (independent LP — depth risk, pool = 52% of DEX liquidity)
- 1 High finding(s) from audit
- 1 Medium finding(s) from audit
- 1 Low finding(s) from audit
Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed
Security Checklist
as of audit · Sep 4Holders
as of audit · Sep 4, 2026- Contractstreasury, vesting, bridge, staking85.3%
- Walletsanonymous holders, free to sell9.7%
- Everyone elsethe rest of the supply5.0%
How holder types affect the score
Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.
Holder balances as recorded by the audit of Sep 4, 2026
Liquidity
as of audit · Sep 4- Curve stblFRAXAnalysed$34.04M51.7%
- Uniswap v4USDT$22.66M34.4%
- Uniswap v4USDT$2.88M4.4%
- Uniswap v3USDC$2.30M3.5%
- Uniswap v4USDC$1.13M1.7%
- Curve stblUSDT$949.6K1.4%
Show 4 more pairs
The 8 remaining pairs hold $284.0K between them and are not listed. The risk score reads depth across every pair.
The LP tokens of the analysed pool are not locked or burned, so whoever holds them can withdraw that liquidity.
0x107e…25bc0x5d37…4bac0x4c34…96fc0x5013…208c0x03e0…a09f0xd033…13da0xe256…f01d0xc9d6…657d0xb88e…c9180xdc32…36adNo privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.
Security Findings
HighCentralized Control over Token Supply
The minter address has the exclusive and unlimited ability to mint new USDe tokens. This centralized control (7.3 Access Control, 7.4 Economic) means that the token's supply and value are highly dependent on the security and integrity of the minter's private keys and the underlying off-chain collateralization mechanism. A compromise of the minter address would allow an attacker to mint arbitrary amounts of tokens, leading to severe inflation and loss of value.H-01
Issue
The minter address has the exclusive and unlimited ability to mint new USDe tokens. This centralized control (7.3 Access Control, 7.4 Economic) means that the token's supply and value are highly dependent on the security and integrity of the minter's private keys and the underlying off-chain collateralization mechanism. A compromise of the minter address would allow an attacker to mint arbitrary amounts of tokens, leading to severe inflation and loss of value.
Fix
Implement robust security measures for the minter address, such as a multi-signature wallet with a high threshold, hardware security modules (HSMs), and strict operational controls. Regularly review and audit the processes surrounding the minter's operations and the off-chain collateral management (7.8 Operations).
Status
Unresolved
MediumOwner's Authority to Change Minter
The contract owner has the authority to change the minter address via the setMinter function (7.3 Access Control). While the owner is a Timelock (7.8 Operations), this still grants significant control over the token's core functionality. A malicious or compromised owner could assign a new minter to an attacker-controlled address, effectively taking over the minting capability.M-01
Issue
The contract owner has the authority to change the minter address via the setMinter function (7.3 Access Control). While the owner is a Timelock (7.8 Operations), this still grants significant control over the token's core functionality. A malicious or compromised owner could assign a new minter to an attacker-controlled address, effectively taking over the minting capability.
Fix
Ensure the Timelock controlling the owner address has a sufficiently long delay and is managed by a decentralized or highly secure governance process (7.5 Governance). Consider implementing additional checks or a multi-signature requirement for critical owner actions like setMinter if the current Timelock setup is deemed insufficient.
Status
Unresolved
LowOwnership Renunciation Disabled
The renounceOwnership function is explicitly overridden to revert, preventing the owner from relinquishing control of the contract (7.3 Access Control). While this prevents accidental renunciation, it also means the owner role can never be permanently removed from the contract, which might be a desired feature for protocols aiming for full decentralization. For a centralized stablecoin, this is likely an intentional design choice to maintain oversight.L-01
Issue
The renounceOwnership function is explicitly overridden to revert, preventing the owner from relinquishing control of the contract (7.3 Access Control). While this prevents accidental renunciation, it also means the owner role can never be permanently removed from the contract, which might be a desired feature for protocols aiming for full decentralization. For a centralized stablecoin, this is likely an intentional design choice to maintain oversight.
Fix
Confirm that preventing ownership renunciation aligns with the long-term decentralization goals of the USDe protocol. If future decentralization is a goal, consider a mechanism to transfer ownership to a zero address or a community-controlled contract, or to enable renunciation, possibly after a significant transition period.
Status
Unresolved
InfoImplied Off-Chain Collateralization
The contract's minting mechanism is permissioned but does not include any on-chain checks or enforcement for collateralization (7.4 Economic, 7.6 External). The stability and value of USDe are implicitly reliant on off-chain reserves and operational procedures managed by the protocol, which are not auditable within the smart contract code. Users must trust the issuer's commitment to maintain the peg through external means.I-01
Issue
The contract's minting mechanism is permissioned but does not include any on-chain checks or enforcement for collateralization (7.4 Economic, 7.6 External). The stability and value of USDe are implicitly reliant on off-chain reserves and operational procedures managed by the protocol, which are not auditable within the smart contract code. Users must trust the issuer's commitment to maintain the peg through external means.
Fix
Clearly communicate the off-chain collateralization strategy, audit reports of reserves, and redemption mechanisms to users. While not a smart contract vulnerability, transparency regarding the external dependencies is crucial for user confidence and understanding of the token's economic model.
Status
Unresolved
Analysis
AI Copilotas of audit · Sep 4The USDe contract demonstrates strong technical security (7.2 Code Security) by inheriting from well-audited OpenZeppelin contracts (ERC20, ERC20Burnable, ERC20Permit, Ownable2Step). The code is straightforward, avoiding complex logic that often leads to vulnerabilities. Standard arithmetic operations are protected by require statements before unchecked blocks, preventing integer overflows/underflows. The architecture (7.1 Architecture) is simple and clear, focusing on a permissioned minting mechanism.
The contract's economic model (7.4 Economic) and governance (7.5 Governance) are highly centralized. The minter role has unlimited power to mint tokens, making the token's supply and value entirely dependent on the minter's integrity and off-chain collateralization. The owner (7.3 Access Control), which is a Timelock (7.8 Operations), can set the minter, thus retaining ultimate control over the minting mechanism. This centralization, while intended for a stablecoin, represents a significant single point of failure if privileged keys are compromised or misused.
The USDe contract is not designed as an upgradeable proxy (7.7 Upgrades). This means there are no upgrade-related risks such as proxy implementation vulnerabilities or storage collisions. However, it also implies that the contract's logic cannot be modified post-deployment without a full redeployment and migration.
Prioritize the robust security of the minter and owner private keys, implementing multi-signature wallets and stringent operational procedures.
Ensure transparency regarding the off-chain collateralization and redemption mechanisms that back the USDe token. While the contract code is sound, the primary risks stem from the centralized control points and their associated operational security.
Contract & Record
Free for any token on the record. It links to this page and always shows the current score and the date it was checked.
- Sep 2, 202650Medium
Score changes are recorded as dated snapshots — history is append-only and cannot be edited.
Would You Like a More Detailed Audit of USDe?
Our AI-powered scanner gives you a deeper, real-time smart contract analysis — free, with every scoring factor shown.
Get Detailed Audit Is this your token? Publish your own audit on this page