The ClankerToken contract is an ERC20 token with extensions for burning, permits, and voting, and includes custom cross-chain mint/burn functionality. The contract is generally well-structured, leveraging battle-tested OpenZeppelin libraries. A key observation is the centralized and immutable _admin role, which controls critical token metadata and a one-time verification flag, posing a single point of failure.
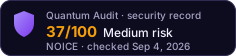
On-chain security analysis — is it a scam or legit?
Is noice Safe?
Not verified
This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →The ClankerToken contract is an ERC20 token with extensions for burning, permits, and voting, and includes custom cross-chain mint/burn functionality.
Read the full analysis- Top-10 concentration > 70%
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top1 unlocked holder = 99.9%
- LP top3 unlocked holders = 100.0%
- 1 High finding(s) from audit
- 1 Low finding(s) from audit
Exact factors
- Top-10 concentration > 70% (81.4% total → 72.2% effective; 66.0% in EOAs, 15.5% in contracts — extreme)
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top1 unlocked holder = 99.9% (independent LP — depth risk, pool = 97% of DEX liquidity)
- LP top3 unlocked holders = 100.0% (independent LP — depth risk, pool = 97% of DEX liquidity)
- 1 High finding(s) from audit
- 1 Low finding(s) from audit
Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed
Security Checklist
as of audit · Sep 4Holders
as of audit · Sep 4, 2026- Contractstreasury, vesting, bridge, staking15.5%
- Walletsanonymous holders, free to sell66.0%
- Everyone elsethe rest of the supply18.6%
How holder types affect the score
Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.
Holder balances as recorded by the audit of Sep 4, 2026
Liquidity
as of audit · Sep 4- Uniswap v3WETHAnalysed$233.9K96.7%
- AerodromeWETH$4.4K1.8%
- AerodromeMAMO$2.3K1.0%
- Uniswap v4ETH$1.2K0.5%
- Hydrex CLAMMWETH$700.0%
The risk score reads depth across every pair.
The LP tokens of the analysed pool are not locked or burned, so whoever holds them can withdraw that liquidity.
0x33e2…c8f90x9a88…bd090xf722…e6860xd29c…a4a00x2ee3…3c7f0xb1da…440b0x33ab…21fa0xe961…9f3dNo privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.
Security Findings
HighCentralized and Immutable Admin Role
The _admin address holds significant control over critical token parameters (e.g., updateImage, updateMetadata, verify) and is set immutably in the constructor without any mechanism for transfer or multi-signature control (7.3 Access Control, 7.5 Governance). This creates a single point of failure; compromise or loss of this key could lead to unauthorized modifications or permanent loss of administrative control, impacting the token's integrity and user trust.H-01
Issue
The _admin address holds significant control over critical token parameters (e.g., updateImage, updateMetadata, verify) and is set immutably in the constructor without any mechanism for transfer or multi-signature control (7.3 Access Control, 7.5 Governance). This creates a single point of failure; compromise or loss of this key could lead to unauthorized modifications or permanent loss of administrative control, impacting the token's integrity and user trust.
Fix
Implement a more robust access control mechanism for the _admin role. This could involve using a multi-signature wallet (e.g., Gnosis Safe) for the admin address or integrating a decentralized governance system. Additionally, consider adding a function to transfer the admin role to a new address, protected by a time-lock or multi-sig, to allow for operational flexibility and recovery.
Status
Unresolved
LowMissing Event for Admin Role Assignment
The _admin address is assigned in the constructor, but no event is emitted to log this critical assignment on-chain (7.8 Operations). While the admin is set during deployment, the absence of an event hinders transparent monitoring and auditing of the initial administrative setup, making it less straightforward to track the initial controller.L-01
Issue
The _admin address is assigned in the constructor, but no event is emitted to log this critical assignment on-chain (7.8 Operations). While the admin is set during deployment, the absence of an event hinders transparent monitoring and auditing of the initial administrative setup, making it less straightforward to track the initial controller.
Fix
Emit an event in the constructor to explicitly log the _admin address upon contract deployment. For example: event AdminSet(address indexed admin); and then emit AdminSet(admin_); in the constructor.
Status
Unresolved
InfoDependency on External Superchain Token Bridge
The crosschainMint and crosschainBurn functions are exclusively controlled by Predeploys.SUPERCHAIN_TOKEN_BRIDGE (7.6 External). This design means the token's supply management and overall cross-chain functionality are directly dependent on the security and integrity of this external bridge. Any vulnerability or compromise within the bridge could directly impact the token's economic model and supply across chains.I-01
Issue
The crosschainMint and crosschainBurn functions are exclusively controlled by Predeploys.SUPERCHAIN_TOKEN_BRIDGE (7.6 External). This design means the token's supply management and overall cross-chain functionality are directly dependent on the security and integrity of this external bridge. Any vulnerability or compromise within the bridge could directly impact the token's economic model and supply across chains.
Fix
While this is a design choice, it is crucial to ensure thorough due diligence on the SUPERCHAIN_TOKEN_BRIDGE contract and its operational security. Understand its audit history, security practices, and potential risks. Implement robust monitoring for bridge activity relevant to this token.
Status
Unresolved
Analysis
AI Copilotas of audit · Sep 4The contract demonstrates strong technical foundations by inheriting from multiple OpenZeppelin ERC20 extensions (ERC20Permit, ERC20Votes, ERC20Burnable), ensuring adherence to established standards and leveraging audited code. Overrides for _update and nonces are correctly implemented, and supportsInterface is properly handled for IERC7802 and other standards (7.2 Code Security). The use of Solidity 0.8.28 mitigates common integer overflow/underflow risks. However, the _admin role is immutable and controls key functions like updateImage and updateMetadata, representing a centralization of control (7.3 Access Control).
The economic model involves an initial fixed supply minted on a specific chain, with crosschainMint and crosschainBurn functions enabling supply movement across chains, restricted to a SUPERCHAIN_TOKEN_BRIDGE (7.4 Economic). This design relies heavily on the security of the external bridge. Governance is highly centralized, with a single _admin address controlling critical parameters such as token image, metadata, and a one-time verification status (7.5 Governance). There is no on-chain governance or multi-signature mechanism for the _admin role, which introduces a significant single point of failure risk.
The ClankerToken contract is implemented as a standard, non-upgradeable ERC20 token (7.7 Upgrades). This design choice eliminates the complexities and potential risks associated with proxy upgrade patterns, providing immutability and predictability for its users. However, it also means that any future changes or bug fixes to the core logic would require a new contract deployment and migration, which can be a complex and costly process.
It is strongly recommended to implement a robust access control mechanism for the _admin role, such as a multi-signature wallet or a time-locked governance contract, to mitigate the risks associated with a single point of failure.
Consider adding an event for the initial assignment of the _admin role to enhance transparency. Furthermore, ensure thorough due diligence on the SUPERCHAIN_TOKEN_BRIDGE to understand its security posture, as the token's cross-chain integrity directly depends on it.
Contract & Record
Free for any token on the record. It links to this page and always shows the current score and the date it was checked.
- Sep 4, 202637Medium
- Aug 12, 202636Medium
Score changes are recorded as dated snapshots — history is append-only and cannot be edited.
Frequently Asked Questions
What is the NOICE contract address?
The noice contract on Base is 0x9cb41fd9dc6891bae8187029461bfaadf6cc0c69. Compare it with the address the project itself publishes before trading: other contracts can carry the same name and ticker.
Is noice a scam?
Quantum Audit's risk score for noice is 37/100 (Medium risk) as of Sep 4, 2026, computed by a deterministic function from on-chain facts — Contract verified: Verified; Ownership: Renounced; Mint: No mint; Liquidity lock: Not locked; Upgradeability: Fixed code. A score is a dated snapshot of those facts, not a guarantee; each one is listed on this page.
Is NOICE liquidity locked?
Liquidity lock: Not locked (as of Sep 4, 2026). Total DEX liquidity: $241.9K.
Who holds NOICE?
As of Sep 4, 2026, the 10 largest holders own 81.4% of the supply. The Holders section on this page shows who they are by holder type.
Would You Like a More Detailed Audit of noice?
Our AI-powered scanner gives you a deeper, real-time smart contract analysis — free, with every scoring factor shown.
Get Detailed Audit Is this your token? Publish your own audit on this page