The OptimismMintableERC20 contract serves as a standard ERC20 token with minting and burning capabilities controlled by a designated bridge. The audit found the contract to be well-structured, adhering to best practices and OpenZeppelin standards. No critical or high-severity vulnerabilities were identified. The primary security consideration is the inherent reliance on the external bridge's security for token supply management.
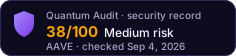
On-chain security analysis — is it a scam or legit?
Is Aave Token Safe?
Not verified
This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →The OptimismMintableERC20 contract serves as a standard ERC20 token with minting and burning capabilities controlled by a designated bridge.
Read the full analysis- Ownership status UNKNOWN
- Mintable supply — no cap found, dilution unbounded
- Top-10 concentration > 30%
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top3 unlocked holders = 88.8%
Exact factors
- Ownership status UNKNOWN (owner could not be resolved)
- Mintable supply — no cap found, dilution unbounded
- Top-10 concentration > 30% (66.3% total → 44.9% effective; 30.7% in EOAs, 35.6% in contracts — moderate)
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top3 unlocked holders = 88.8% (independent LP — depth risk, pool = 81% of DEX liquidity)
Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed
Security Checklist
as of audit · Sep 4Holders
as of audit · Sep 4, 2026- Contractstreasury, vesting, bridge, staking35.6%
- Walletsanonymous holders, free to sell30.7%
- Everyone elsethe rest of the supply33.7%
How holder types affect the score
Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.
Holder balances as recorded by the audit of Sep 4, 2026
Liquidity
as of audit · Sep 4- AerodromeWETHAnalysed$1.24M80.9%
- Uniswap v3WETH$135.8K8.9%
- Quickswap v4WETH$56.0K3.7%
- PancakeswapWETH$39.7K2.6%
- Uniswap v3USDC$31.4K2.1%
- Uniswap v4UNI$15.4K1.0%
Show 4 more pairs
The 10 remaining pairs hold $1.6K between them and are not listed. The risk score reads depth across every pair.
The LP tokens of the analysed pool are not locked or burned, so whoever holds them can withdraw that liquidity.
0xd392…74700x7d27…fd550x9f6e…0b070x75fc…38360x02cb…8ce80xae6f…8e730xdf09…72010x4efc…b6920xd82f…e9620x3714…acfeNo privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.
Security Findings
InfoReliance on External Bridge Security
The mint and burn functions, which control the token's supply, are exclusively callable by the BRIDGE address. This design is fundamental for a cross-chain mintable token, but it means the security and integrity of the token's supply are entirely dependent on the security of the external BRIDGE contract. A compromise of the BRIDGE would allow arbitrary minting or burning of tokens, directly impacting the token's value and trust.I-01
Issue
The mint and burn functions, which control the token's supply, are exclusively callable by the BRIDGE address. This design is fundamental for a cross-chain mintable token, but it means the security and integrity of the token's supply are entirely dependent on the security of the external BRIDGE contract. A compromise of the BRIDGE would allow arbitrary minting or burning of tokens, directly impacting the token's value and trust.
Fix
Ensure the BRIDGE contract is thoroughly audited, robustly secured, and follows best practices for access control, operational security, and incident response. Implement multi-signature control or time-locks for critical operations within the bridge if applicable.
Status
Unresolved
InfoImmutable Critical Parameters
The REMOTE_TOKEN, BRIDGE, and DECIMALS variables are declared as immutable and are set only once during contract construction. This prevents any post-deployment modification of these critical parameters, enhancing the contract's security, predictability, and immutability of its core configuration.I-02
Issue
The REMOTE_TOKEN, BRIDGE, and DECIMALS variables are declared as immutable and are set only once during contract construction. This prevents any post-deployment modification of these critical parameters, enhancing the contract's security, predictability, and immutability of its core configuration.
Fix
Continue to utilize immutable variables for critical parameters that should not change after deployment, as this is a strong security practice.
Status
Unresolved
InfoAdherence to ERC Standards and Backward Compatibility
The contract correctly implements the ERC20 standard for token functionality and the ERC165 standard for interface introspection. It also includes legacy interfaces (ILegacyMintableERC20) and corresponding getter functions for backward compatibility within the Optimism ecosystem, ensuring broad interoperability without compromising current standards.I-03
Issue
The contract correctly implements the ERC20 standard for token functionality and the ERC165 standard for interface introspection. It also includes legacy interfaces (ILegacyMintableERC20) and corresponding getter functions for backward compatibility within the Optimism ecosystem, ensuring broad interoperability without compromising current standards.
Fix
Maintain strict adherence to relevant ERC standards and ensure backward compatibility where necessary, as demonstrated, to support ecosystem evolution and integration.
Status
Unresolved
InfoAbsence of Reentrancy and Arithmetic Vulnerabilities
The contract does not perform external calls to untrusted addresses after state changes, effectively mitigating reentrancy risks. Furthermore, by inheriting from OpenZeppelin's ERC20 library and operating in Solidity 0.8.15, the contract benefits from built-in overflow/underflow checks, preventing common arithmetic vulnerabilities in token operations.I-04
Issue
The contract does not perform external calls to untrusted addresses after state changes, effectively mitigating reentrancy risks. Furthermore, by inheriting from OpenZeppelin's ERC20 library and operating in Solidity 0.8.15, the contract benefits from built-in overflow/underflow checks, preventing common arithmetic vulnerabilities in token operations.
Fix
Continue to leverage secure and audited libraries like OpenZeppelin and Solidity's native safety features to prevent common vulnerabilities.
Status
Unresolved
Analysis
AI Copilotas of audit · Sep 4The technical implementation of the OptimismMintableERC20 contract is robust, leveraging OpenZeppelin's battle-tested ERC20 library. Key security features include the use of immutable variables for critical addresses like BRIDGE and REMOTE_TOKEN (7.2 Code Security). Access control for mint and burn functions is strictly enforced via the onlyBridge modifier (7.3 Access Control). The contract exhibits no reentrancy vulnerabilities or integer overflow/underflow issues due to Solidity 0.8.x's default checks and careful design.
The economic model of the OptimismMintableERC20 token is straightforward, with its supply directly managed by a designated BRIDGE contract (7.4 Economic). This design is intentional for cross-chain functionality, meaning the token's integrity is inherently tied to the security of the external bridge. There are no internal governance mechanisms within this contract (7.5 Governance), simplifying its attack surface but centralizing control over token supply to the bridge.
The OptimismMintableERC20 contract is not designed as an upgradeable proxy, nor does it contain any self-upgrade mechanisms (7.7 Upgrades). This eliminates upgrade-related risks such as proxy storage collisions or logic errors during upgrades. The contract's version constant is for off-chain tooling and does not imply on-chain upgradeability.
The OptimismMintableERC20 contract is well-implemented and secure for its intended purpose.
The primary recommendation is to ensure the utmost security and rigorous auditing of the BRIDGE contract that controls the minting and burning of these tokens, as its compromise would directly impact the token's integrity. Additionally, maintain consistent development practices, including thorough testing and adherence to established security patterns, for any future modifications or related contracts.
Contract & Record
Free for any token on the record. It links to this page and always shows the current score and the date it was checked.
- Sep 4, 202638Medium
- Jul 23, 202642Medium
- Jul 23, 202633Low
Score changes are recorded as dated snapshots — history is append-only and cannot be edited.
Would You Like a More Detailed Audit of Aave Token?
Our AI-powered scanner gives you a deeper, real-time smart contract analysis — free, with every scoring factor shown.
Get Detailed Audit Is this your token? Publish your own audit on this page