The LabToken contract implements a standard ERC20 token with burnable functionality, leveraging battle-tested OpenZeppelin libraries. The contract's simplicity and reliance on well-audited components contribute to a low technical risk profile. The primary consideration is the centralized initial token distribution, where the entire supply is minted to the deployer, which introduces a governance and economic risk depending on the project's distribution strategy.
On-chain security analysis — is it a scam or legit?
Is LAB Safe?
Not verified
This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →The LabToken contract implements a standard ERC20 token with burnable functionality, leveraging battle-tested OpenZeppelin libraries.
Read the full analysis- Ownership status UNKNOWN
- Top-10 concentration > 30%
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top1 unlocked holder = 97.3%
- LP top3 unlocked holders = 99.9%
- 1 Low finding(s) from audit
Exact factors
- Ownership status UNKNOWN (owner could not be resolved)
- Top-10 concentration > 30% (63.7% total → 36.6% effective; 18.5% in EOAs, 45.2% in contracts — moderate)
- Liquidity not locked, but no owner/deployer address holds LP — market-depth risk, not rug risk
- LP top1 unlocked holder = 97.3% (independent LP — depth risk, pool = 73% of DEX liquidity)
- LP top3 unlocked holders = 99.9% (independent LP — depth risk, pool = 73% of DEX liquidity)
- 1 Low finding(s) from audit
Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed
Security Checklist
as of audit · Sep 4Holders
as of audit · Sep 4, 2026- Contractstreasury, vesting, bridge, staking45.2%
- Walletsanonymous holders, free to sell18.5%
- Everyone elsethe rest of the supply36.3%
How holder types affect the score
Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.
Holder balances as recorded by the audit of Sep 4, 2026
Liquidity
as of audit · Sep 4- Pancakeswap v3USDTAnalysed$140.5K73.2%
- UniswapUSDT$48.4K25.2%
- UniswapUSDT$2.5K1.3%
- Pancakeswap v3USDT$3870.2%
- TopazWBNB$2370.1%
- Pancakeswap v3WBNB$240.0%
Show 2 more pairs
The risk score reads depth across every pair.
The LP tokens of the analysed pool are not locked or burned, so whoever holds them can withdraw that liquidity.
0xf949…02980x9d56…e0ee0xbc7a…3e710xce13…f41c0xee9b…81b00x8e0a…76c10x9fd1…575b0xbefc…550e0x478b…cdc50xae8a…d7bdNo privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.
Security Findings
LowCentralized Initial Token Distribution
The LabToken contract's constructor mints the entire initial supply of 1,000,000,000 tokens to the msg.sender (the contract deployer). This design choice results in 100% of the token supply being held by a single address immediately after deployment. While common, this centralization can pose a governance and economic risk if the deployer's address is compromised or if the distribution strategy is not transparently executed.L-01
Issue
The LabToken contract's constructor mints the entire initial supply of 1,000,000,000 tokens to the msg.sender (the contract deployer). This design choice results in 100% of the token supply being held by a single address immediately after deployment. While common, this centralization can pose a governance and economic risk if the deployer's address is compromised or if the distribution strategy is not transparently executed.
Fix
Implement a clear and transparent plan for the distribution of the initially minted tokens. Consider using a multi-signature wallet to manage the deployer's address holding the tokens, or distribute tokens to multiple addresses/contracts (e.g., vesting contracts, liquidity pools) immediately after deployment to reduce single-point-of-failure risk and enhance decentralization.
Status
Unresolved
InfoReliance on Standard OpenZeppelin Libraries
The LabToken contract extensively utilizes well-audited and battle-tested OpenZeppelin contracts (ERC20, ERC20Burnable, Context, etc.). This approach significantly enhances the security posture of the contract by relying on code that has undergone extensive peer review and real-world usage, minimizing the risk of common vulnerabilities.I-01
Issue
The LabToken contract extensively utilizes well-audited and battle-tested OpenZeppelin contracts (ERC20, ERC20Burnable, Context, etc.). This approach significantly enhances the security posture of the contract by relying on code that has undergone extensive peer review and real-world usage, minimizing the risk of common vulnerabilities.
Fix
No specific recommendation. Continue to monitor OpenZeppelin updates and security advisories for any potential issues in the underlying libraries.
Status
Unresolved
InfoImmutability of Contract Logic
The LabToken contract is implemented as a standard, non-upgradeable contract. Once deployed, its logic cannot be modified. This immutability ensures that the contract's behavior is fixed and predictable, eliminating risks associated with upgrade mechanisms (e.g., proxy implementation bugs, insecure upgrade paths).I-02
Issue
The LabToken contract is implemented as a standard, non-upgradeable contract. Once deployed, its logic cannot be modified. This immutability ensures that the contract's behavior is fixed and predictable, eliminating risks associated with upgrade mechanisms (e.g., proxy implementation bugs, insecure upgrade paths).
Fix
No specific recommendation. Acknowledge that any future changes or bug fixes would require deploying a new contract and migrating token holders, which can be a complex process.
Status
Unresolved
InfoAbsence of Custom Business Logic
The LabToken contract does not introduce any custom business logic beyond the standard ERC20 and ERC20Burnable functionalities provided by OpenZeppelin. This simplicity reduces the overall attack surface and the likelihood of introducing new, project-specific vulnerabilities, contributing to a higher level of security.I-03
Issue
The LabToken contract does not introduce any custom business logic beyond the standard ERC20 and ERC20Burnable functionalities provided by OpenZeppelin. This simplicity reduces the overall attack surface and the likelihood of introducing new, project-specific vulnerabilities, contributing to a higher level of security.
Fix
No specific recommendation. Maintain this minimalist approach if the project's requirements do not necessitate additional complex features, as it inherently reduces security risks.
Status
Unresolved
Analysis
AI Copilotas of audit · Sep 4The technical architecture (7.1 Architecture) of LabToken is robust, inheriting directly from OpenZeppelin's ERC20 and ERC20Burnable contracts. This significantly reduces the attack surface and leverages extensively audited code for core token functionalities. Code security (7.2 Code Security) is high, with standard implementations for transfers, approvals, and burning, including proper handling of integer overflows/underflows via OpenZeppelin's unchecked blocks and require statements. Access control (7.3 Access Control) is limited to standard ERC20 roles (owner, spender) without custom permissions, which simplifies the design but means no additional administrative controls.
The economic model (7.4 Economic) involves an initial mint of 1,000,000,000 tokens to the contract deployer (msg.sender) in the constructor. This design choice centralizes 100% of the token supply with a single address, presenting a significant governance risk (7.5 Governance) if not managed transparently. While this is a common pattern for initial token distribution, it places full control over the token's immediate supply and potential market impact in the hands of the deployer. There are no external dependencies (7.6 External) that could introduce economic or governance risks.
The LabToken contract is not designed with upgradeability features (7.7 Upgrades), meaning its logic is immutable once deployed. This eliminates risks associated with upgrade mechanisms, such as proxy implementation bugs or insecure upgrade paths. However, it also means that any future bug fixes or feature enhancements would require a complete redeployment and migration of token holders. Operations (7.8 Operations) are straightforward, as there are no complex administrative functions beyond standard ERC20 operations.
It is recommended to clearly communicate the token distribution strategy to the community, especially regarding the initial centralized mint.
Consider implementing a multi-signature wallet for the deployer address if the tokens are intended for long-term project funding or controlled distribution, to mitigate single-point-of-failure risks. For future projects, evaluate whether a more decentralized initial distribution or a phased release mechanism aligns better with project goals and community expectations.
Contract & Record
Free for any token on the record. It links to this page and always shows the current score and the date it was checked.
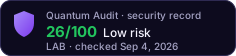
- Sep 4, 202626Low
- Aug 11, 202625Low
Score changes are recorded as dated snapshots — history is append-only and cannot be edited.
Would You Like a More Detailed Audit of LAB?
Our AI-powered scanner gives you a deeper, real-time smart contract analysis — free, with every scoring factor shown.
Get Detailed Audit Is this your token? Publish your own audit on this page