This audit covers a truncated Solidity source code snippet, identified as OpenZeppelin's AccessControl contract. The provided code implements a standard role-based access control mechanism. While the core OpenZeppelin implementation is robust and well-audited, the audit scope is limited by the incomplete source. The primary risks identified are related to the governance implications of the powerful DEFAULT_ADMIN_ROLE and general best practices for critical operations in systems utilizing such access control.
On-chain security analysis — is it a scam or legit?
Is ARK Safe?
Not verified
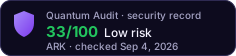
This record has not gone through deep verification and is not being monitored. The score is a dated snapshot — the token’s risk can change at any time.Own this token? Put it under verification →This audit covers a truncated Solidity source code snippet, identified as OpenZeppelin's AccessControl contract.
Read the full analysis- Ownership not renounced
- Mintable supply — no cap found, dilution unbounded
- Top-10 concentration > 30%
- 2 Low finding(s) from audit
Exact factors
- Ownership NOT renounced (admin/mint authority retained)
- Mintable supply — no cap found, dilution unbounded
- Top-10 concentration > 30% (97.7% total → 40.6% effective; 2.5% in EOAs, 95.2% in contracts — moderate)
- 2 Low finding(s) from audit
Each factor is an on-chain fact recorded at the time of this analysis. The score is computed from them by a deterministic function, so the same contract returns the same score for anyone who runs the audit. How scores are computed
Security Checklist
as of audit · Sep 4Holders
as of audit · Sep 4, 2026- Contractstreasury, vesting, bridge, staking95.2%
- Walletsanonymous holders, free to sell2.5%
- Everyone elsethe rest of the supply2.3%
How holder types affect the score
Share held by contracts — treasury, vesting, bridge or staking — is discounted against share held by wallets when the score is computed: a contract cannot decide to sell the way an anonymous holder can, though it can still be drained or voted to sell. Effective concentration is the figure the risk score is actually calculated from.
Holder balances as recorded by the audit of Sep 4, 2026
Liquidity
as of audit · Sep 4The risk score reads depth across every pair.
The LP tokens of the analysed pool are locked or burned.
0xfb1f…75760x902e…f7920x89c8…a46a0x4127…88550x037c…643f0xca8f…d1f80x01e7…5d2d0x2511…88beNo privileged address appears among these holders: the unlocked liquidity sits with independent providers, not with the deployer.
Security Findings
LowLack of Time-Locks for Critical Role Changes
While AccessControl provides a robust mechanism for managing roles, it does not inherently include time-lock functionality for critical operations such as granting or revoking sensitive roles. For roles that control significant protocol parameters, funds, or upgradeability, immediate changes could be exploited if an admin key is compromised or a malicious actor gains control.L-01
Issue
While AccessControl provides a robust mechanism for managing roles, it does not inherently include time-lock functionality for critical operations such as granting or revoking sensitive roles. For roles that control significant protocol parameters, funds, or upgradeability, immediate changes could be exploited if an admin key is compromised or a malicious actor gains control.
Fix
For any roles that have the ability to perform critical operations (e.g., modifying protocol fees, pausing contracts, or upgrading logic), consider implementing a time-lock mechanism on top of the grantRole and revokeRole functions. This would introduce a delay before changes take effect, allowing for community scrutiny or emergency intervention.
Status
Unresolved
LowAbsence of Emergency Pause Functionality
The AccessControl contract itself does not include an emergency pause mechanism. In complex DeFi protocols, the ability to pause certain functionalities (e.g., deposits, withdrawals, trading) can be crucial to mitigate damage during an exploit, critical bug discovery, or market instability. Without such a mechanism, the protocol may be vulnerable to ongoing attacks or irreversible losses.L-02
Issue
The AccessControl contract itself does not include an emergency pause mechanism. In complex DeFi protocols, the ability to pause certain functionalities (e.g., deposits, withdrawals, trading) can be crucial to mitigate damage during an exploit, critical bug discovery, or market instability. Without such a mechanism, the protocol may be vulnerable to ongoing attacks or irreversible losses.
Fix
Consider integrating an emergency pause mechanism (e.g., OpenZeppelin's Pausable module) into the contracts that inherit AccessControl and manage critical protocol operations. This pause functionality should be controlled by a specific, highly secured role (e.g., a multi-sig wallet) to prevent abuse.
Status
Unresolved
InfoCentralization Risk of DEFAULT_ADMIN_ROLE
The DEFAULT_ADMIN_ROLE in the AccessControl contract holds significant power, as it can grant and revoke any other role, including itself. If this role is controlled by a single external owned account (EOA), it represents a single point of failure and a high centralization risk. A compromise of this EOA could lead to full control over the protocol's access management.I-01
Issue
The DEFAULT_ADMIN_ROLE in the AccessControl contract holds significant power, as it can grant and revoke any other role, including itself. If this role is controlled by a single external owned account (EOA), it represents a single point of failure and a high centralization risk. A compromise of this EOA could lead to full control over the protocol's access management.
Fix
It is strongly recommended that the DEFAULT_ADMIN_ROLE be assigned to a robust multi-signature wallet (e.g., Gnosis Safe) requiring multiple approvals for any transaction. This distributes control and significantly reduces the risk of a single point of compromise.
Status
Unresolved
InfoIncomplete Source Code Provided for Audit
The provided source code snippet is a flattened version of OpenZeppelin's AccessControl and its dependencies, but it appears to be truncated. The audit was conducted based solely on the provided code, which may not represent the entire codebase of the 'ARK Protocol' or the specific contract being deployed. This limits the scope of the audit and prevents a comprehensive review of all potential interactions and custom logic.I-02
Issue
The provided source code snippet is a flattened version of OpenZeppelin's AccessControl and its dependencies, but it appears to be truncated. The audit was conducted based solely on the provided code, which may not represent the entire codebase of the 'ARK Protocol' or the specific contract being deployed. This limits the scope of the audit and prevents a comprehensive review of all potential interactions and custom logic.
Fix
For a complete security assessment, the full and complete source code of all relevant contracts, including any inheriting contracts or custom logic built on top of AccessControl, should be provided. This ensures all potential attack vectors and interactions can be thoroughly analyzed.
Status
Unresolved
Analysis
AI Copilotas of audit · Sep 4The contract utilizes OpenZeppelin's AccessControl module, which is a well-audited and widely adopted standard for implementing role-based access control (7.2 Code Security). This provides a robust and secure foundation for managing permissions within the protocol. The implementation correctly uses bytes32 identifiers for roles and enforces admin role requirements for grantRole and revokeRole (7.3 Access Control). No custom logic or complex interactions were observed that would introduce new technical vulnerabilities.
The AccessControl pattern inherently introduces governance considerations, particularly concerning the DEFAULT_ADMIN_ROLE (7.5 Governance). This role possesses the power to grant and revoke any other role, including itself, making it a critical point of control. If this role is controlled by a single entity or an easily compromised EOA, it presents a significant centralization risk (7.4 Economic). For example, a compromised admin could grant themselves sensitive roles, leading to unauthorized asset control or protocol manipulation. Implementing multi-signature wallets for the DEFAULT_ADMIN_ROLE is crucial to mitigate this risk.
The provided contract is a standard AccessControl implementation and is not designed to be upgradeable (7.7 Upgrades). There are no proxy patterns (e.g., UUPS, Transparent) or upgrade-specific logic present in the code. This means the contract's logic is immutable once deployed, eliminating risks associated with upgradeability such as proxy misconfigurations or malicious upgrade implementations.
For any system built upon this AccessControl contract, it is paramount to secure the DEFAULT_ADMIN_ROLE using a robust multi-signature wallet.
Additionally, consider implementing time-locks for critical operations, especially those involving role changes for sensitive functions, to provide a window for review and potential intervention. Finally, evaluate the need for an emergency pause mechanism in the overall protocol design to mitigate unforeseen risks.
Contract & Record
Free for any token on the record. It links to this page and always shows the current score and the date it was checked.
- Jul 23, 202633Low
- Jul 23, 202637Medium
Score changes are recorded as dated snapshots — history is append-only and cannot be edited.
Would You Like a More Detailed Audit of ARK?
Our AI-powered scanner gives you a deeper, real-time smart contract analysis — free, with every scoring factor shown.
Get Detailed Audit Is this your token? Publish your own audit on this page